You Are Not Too Small to Be a Target
“We’re too small to be a target.” It’s a common thing to hear from business owners here on Florida’s Space Coast, and it makes sense on the surface. You’re not a hospital system or a Fortune 500 company. Why would a hacker bother with you?
Here’s the uncomfortable answer. Verizon’s 2026 Data Breach Investigations Report, the industry’s largest annual study of real world breaches, found that attackers are getting in through unpatched software more often than through stolen passwords. That shift matters for every business with a network. The door attackers use most often is one that’s sometimes left unlocked because nobody got around to closing it. Being small doesn’t make that door less inviting.
Why “Too Small to Be a Target” Feels True
It’s a reasonable assumption if you think about hacking the way movies portray it: a hooded figure hand picking a specific company to break into. That kind of targeted attack does happen, but it’s not what’s hitting most small businesses.
The 2026 DBIR makes an important point that people often miss: most attacks aren’t personal. They’re opportunistic. Attackers scan the internet for unpatched systems and exposed credentials. Whoever has the gap can get hit, regardless of industry or revenue. Your business doesn’t need to be flashy to a hacker. It just needs to be reachable.
The Numbers Worth Knowing
A few findings from this year’s report are worth sitting with, because they explain why small businesses have become such a common target.
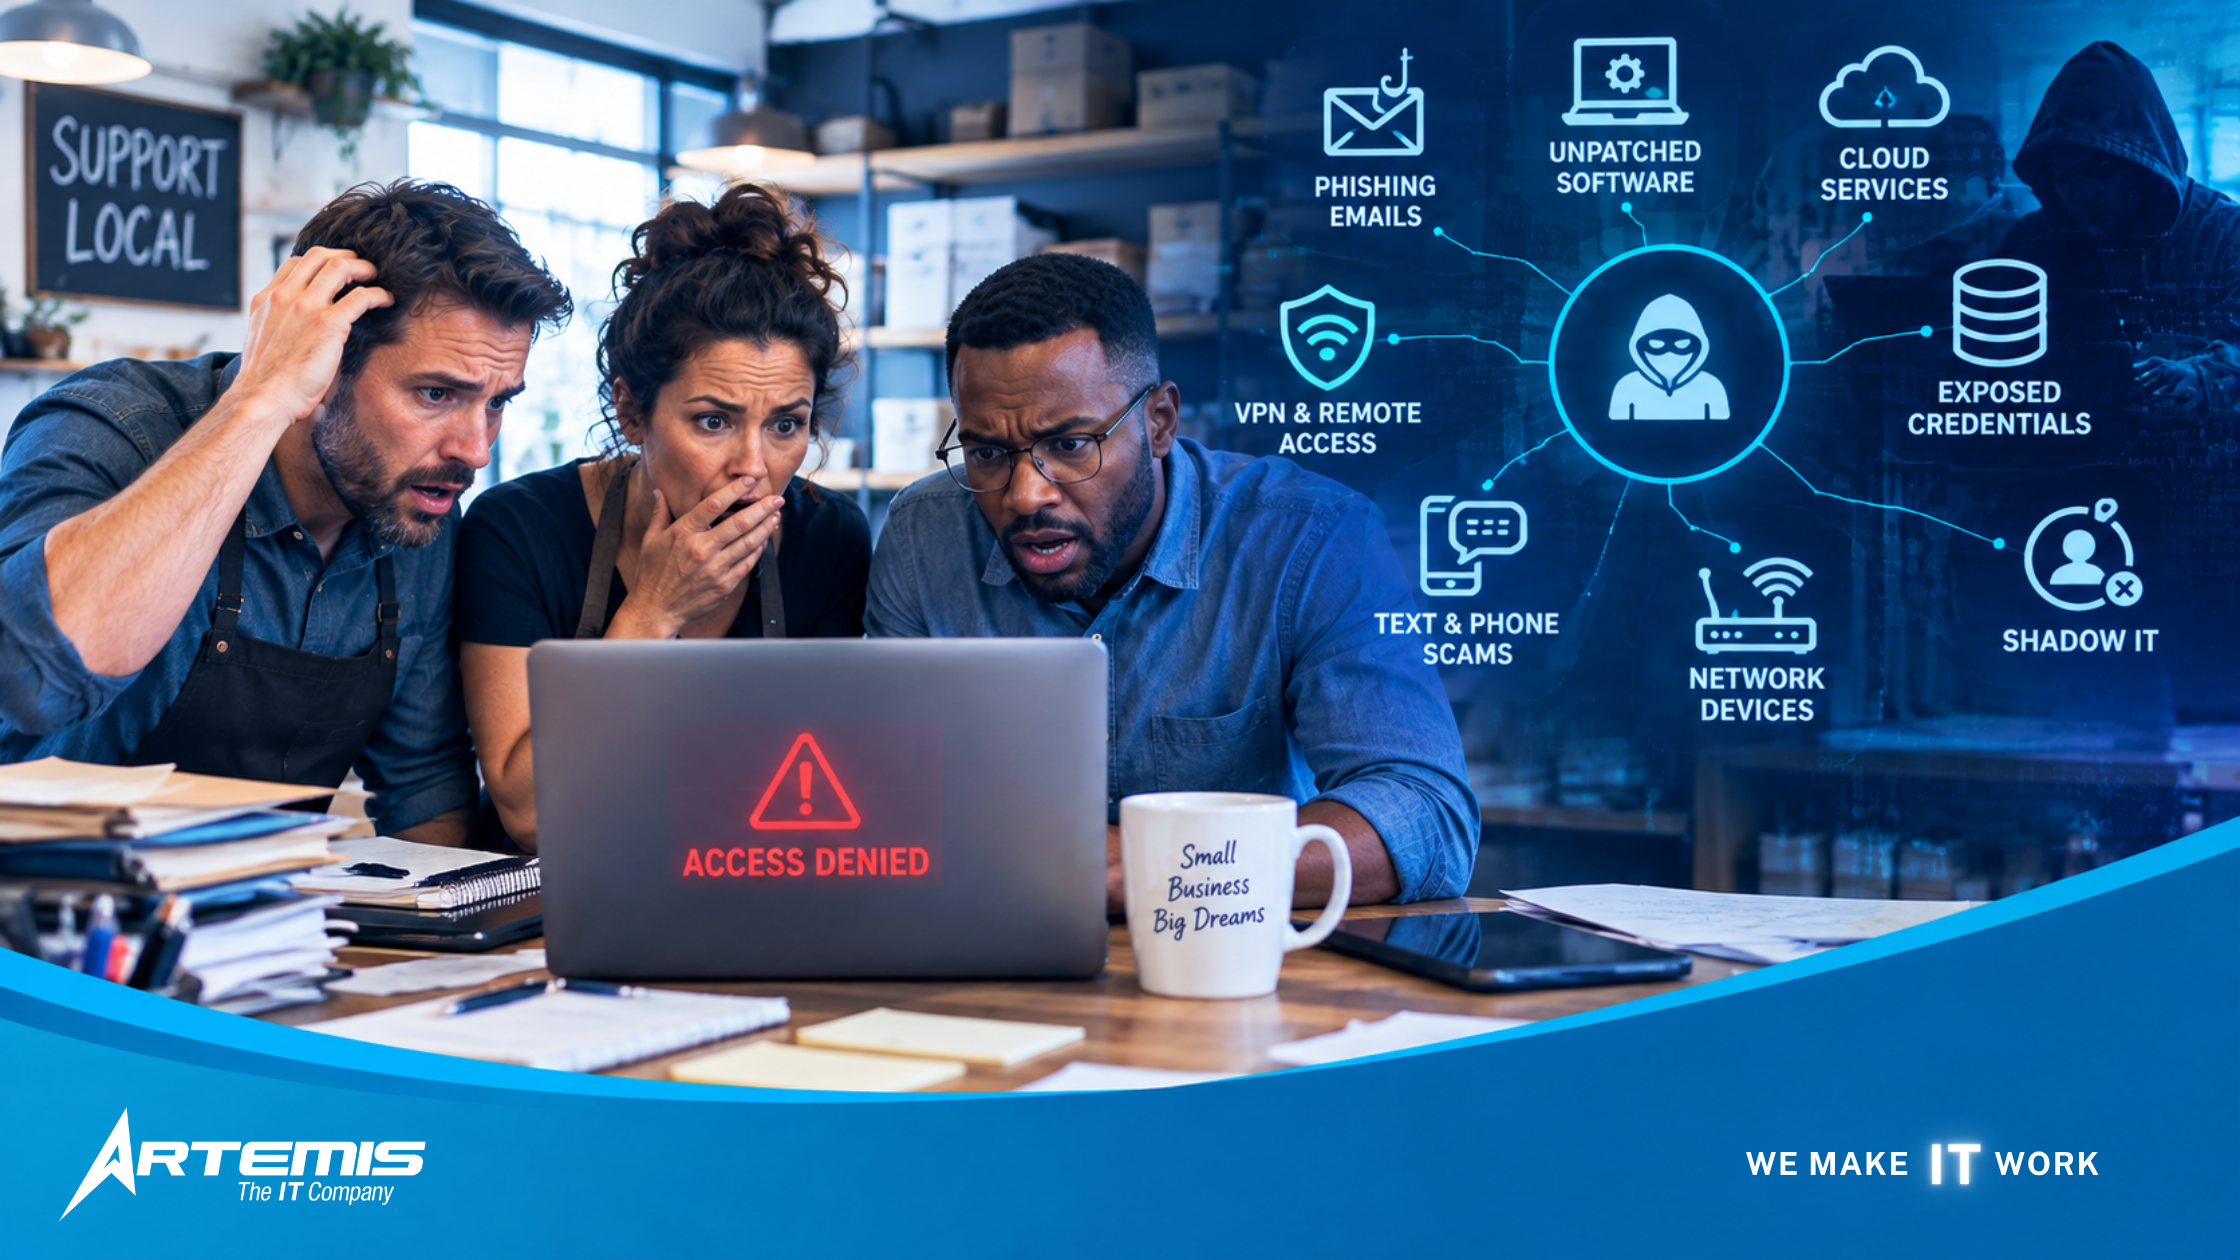
- Exploiting unpatched software has overtaken stolen passwords as the number one way attackers get in, according to Verizon’s report. It’s the first time that’s happened in the study’s history. Unpatched, internet facing systems like VPNs and remote access tools are the biggest opening right now.
- 62 percent of breaches still involve some form of human error, like a clicked link or reused password, according to the Cyber Readiness Institute’s summary of the report. Technical gaps and human mistakes both matter. It isn’t one or the other.
- Small organizations make up the large majority of ransomware victims tracked in the report. That trend has been building for a few years. The exact share varies depending on how it’s measured and who’s summarizing it, but the direction is consistent. Small doesn’t mean overlooked.
- Attackers are also increasingly reaching people through text messages and phone calls rather than just email, catching people off guard because fewer people expect to be scammed that way.
None of this means small businesses are careless. It means small businesses are often easier, not because of anything they did wrong, but because bigger companies have entire teams dedicated to closing these gaps and smaller ones usually don’t.
There Is Good News Here Too
The same report found that 69 percent of small businesses hit with ransomware refused to pay, because they had backups they could actually restore from. That’s the part worth paying attention to. The businesses that came out the other side of an attack in the best shape weren’t necessarily the ones that never got hit. They were the ones that were ready when it happened.
That’s really the whole point of cybersecurity for a small business. It’s not about becoming an impossible target. Nobody is. It’s about making sure that if something gets through, it’s a bad afternoon instead of a catastrophic event.
What Actually Moves the Needle
If you want to reduce your risk without turning your business upside down, a few things consistently make the biggest difference.
- Multi factor authentication on email, banking, and anything with login credentials. This can block a significant share of attacks that rely on stolen passwords.
- Regular patching, especially on anything facing the internet, like VPNs and remote access tools. Attackers now exploit unpatched software more often than stolen passwords, making this a critical part of your security plan.
- Backups that are actually tested, not just scheduled. A backup nobody has verified in a year is a hope, not a plan.
- A little bit of employee training, focused on newer tricks like text message and phone-based scams. Don’t limit training to the email phishing examples everyone has already seen a hundred times.
None of these require a massive budget or an overnight transformation. They require attention and a partner who watches for the gaps, so you don’t have to think about them every day.
The Bottom Line
If you take one thing from this, let it be this: you are not too small to be a target. Being small doesn’t make you invisible to attackers. Attackers don’t care how many employees you have. They exploit the same gaps, whether you have 10 employees or 1,000. The good news is that closing them doesn’t take an enterprise budget, just a clear plan and some consistency.
If you’re not sure where your business stands right now, let’s talk about IT.